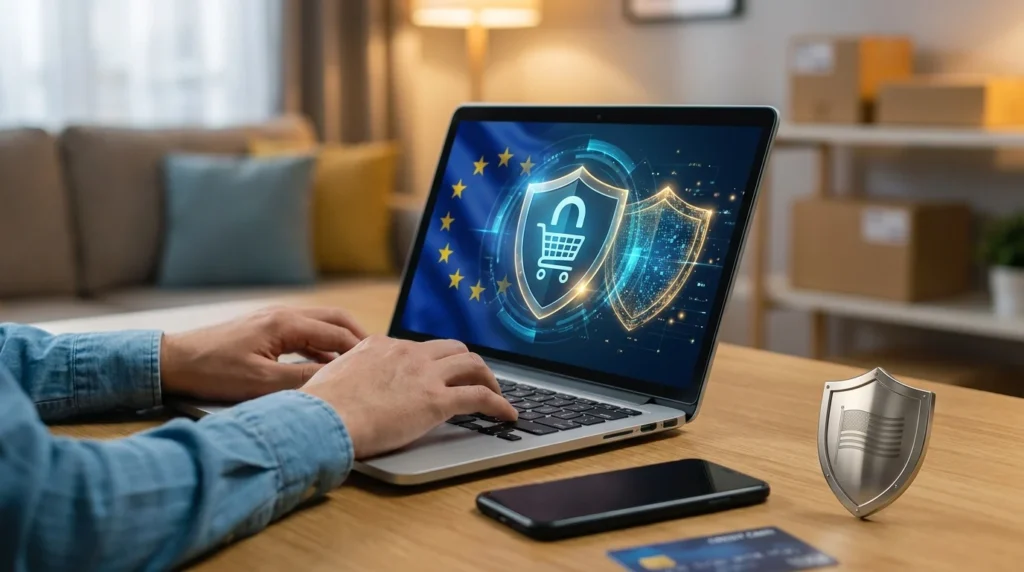
The General Data Protection Regulation (GDPR) has significantly reshaped the landscape of online shopping. This regulation, which came into effect in May 2018, aims to protect the privacy and personal data of individuals within the European Union. Understanding GDPR online shopping implications is crucial for both consumers and retailers.
The Basics of GDPR
GDPR stands for the General Data Protection Regulation, a comprehensive data protection law in the EU. It mandates that businesses must protect the personal data and privacy of EU citizens for transactions that occur within EU member states. This regulation applies to all companies that process personal data of individuals residing in the EU, regardless of the company’s location.
How GDPR Affects Online Retailers
For online retailers, GDPR imposes strict data protection requirements. Retailers must obtain explicit consent from users before collecting any personal data. They are also required to provide clear information on how the data will be used. Failure to comply with these requirements can result in hefty fines, making it essential for businesses to review their data handling practices.
Enhancing Consumer Trust
One of the positive impacts of GDPR on online shopping is the enhancement of consumer trust. By ensuring that companies are transparent about their data usage, consumers feel more confident in sharing their information. This transparency helps build stronger customer relationships and encourages more secure shopping experiences.
Challenges Faced by Businesses
Complying with GDPR presents several challenges for businesses. They need to invest in new technologies and processes to ensure compliance, which can be costly. Additionally, businesses must regularly update their privacy policies and data management practices to align with GDPR requirements. These challenges necessitate a strategic approach to data management and customer interactions.
The Role of GDPR in Data Breach Prevention
GDPR plays a crucial role in preventing data breaches. It requires businesses to implement robust security measures to protect personal data. In case of a data breach, companies must notify the relevant authorities within 72 hours. This prompt reporting helps mitigate the impact of data breaches and protects consumers from potential harm.
Future Implications of GDPR
Looking ahead, GDPR will continue to influence the online shopping environment. As technology evolves, the regulation may undergo modifications to address new challenges in data protection. Companies must stay informed about these changes to ensure ongoing compliance and protect consumer data.
For more insights on securing your online shopping experience, you can explore our articles on protecting your personal information while shopping online and understanding secure payment methods for online shopping.
Impact on Marketing Practices
One significant area where GDPR has made its mark is on the marketing strategies employed by online retailers. The regulation has imposed stringent conditions regarding how customer data can be used for marketing purposes. Prior to GDPR, many businesses relied heavily on broad data collection techniques, such as purchasing third-party data lists or employing cookies to track consumer behavior across the web for targeted advertising. Under GDPR, these practices are tightly regulated.
Retailers are now required to obtain explicit consent from consumers before using their data for marketing activities. This means consumers must actively opt-in to receive marketing communications, and businesses must clearly specify how they will use the data. This shift has forced companies to adopt more transparent and consumer-friendly marketing practices, focusing on permission-based marketing. As a result, businesses may need to invest more in strategies that foster genuine consumer interest and consent, such as personalized content, loyalty programs, and email marketing that respects privacy preferences.
Data Minimization and Retention Policies
GDPR emphasizes the principle of data minimization, which requires businesses to collect only the data that is necessary for a specific purpose. This principle has led online retailers to critically evaluate the data they collect and retain. The regulation encourages companies to consider whether the data they gather is truly essential to their operations and to avoid excessive data collection that could put consumer privacy at risk.
Additionally, GDPR mandates that personal data should not be kept for longer than necessary. This has prompted businesses to establish clear data retention policies, detailing how long different types of data will be stored and when it will be securely deleted. Retailers must ensure their data storage practices comply with these requirements, which may involve regularly auditing their databases and implementing automated systems to manage data lifecycle processes.
By adhering to data minimization and retention principles, companies not only comply with GDPR but also reduce the risk of data breaches and improve data management efficiency. This approach helps build trust with customers, who are more likely to engage with businesses that demonstrate a commitment to protecting their personal information.